GRC Analyst Resume Examples & Free GRC Resume Template (PDF, Word)

Free GRC Analyst resume template from an ex-Google recruiter, with 3 finished GRC resume examples (junior to principal) and a 6-step guide to the format, summary, bullets, skills, keywords & metrics that compliance recruiters screen for.

4.9 5.0
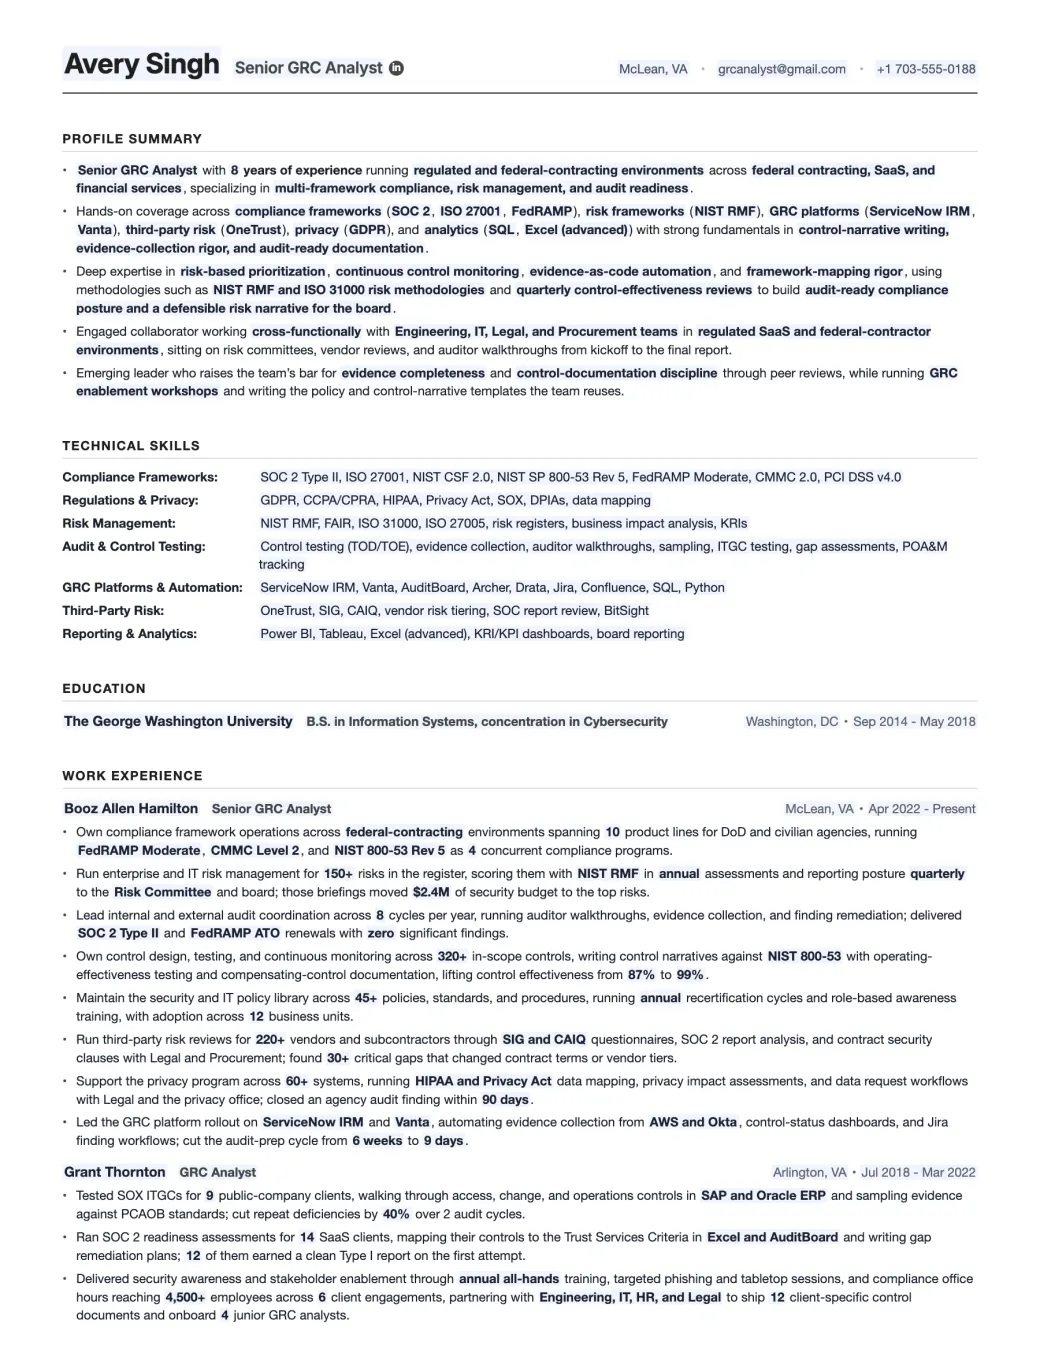
The GRC Analyst resume template, filled in: profile summary, technical skills, education and work experience with the editable placeholders highlighted
Emmanuel Gendre Ex-Google recruiter / Tech resume writer Updated Free, ATS-friendly, no signup

Interactive resume template generator

Interactive GRC Analyst Resume Template

Fill in the side panel, then download your resume as a PDF or a Word file.

Edits update live as you type. Toggle Edit to rewrite paper text directly.

Edit mode is on. Click anywhere on the resume to rewrite text. Side-panel placeholders still update live.

Avery Singh Senior GRC Analyst

McLean, VA • grcanalyst@gmail.com • +1 703-555-0188

Profile Summary

  • Senior GRC Analyst with 8 years of experience running regulated and federal-contracting environments across federal contracting, SaaS, and financial services, specializing in multi-framework compliance, risk management, and audit readiness.
  • Hands-on coverage across compliance frameworks (SOC 2, ISO 27001, FedRAMP), risk frameworks (NIST RMF), GRC platforms (ServiceNow IRM, Vanta), third-party risk (OneTrust), privacy (GDPR), and analytics (SQL, Excel (advanced)) with strong fundamentals in control-narrative writing, evidence-collection rigor, and audit-ready documentation.
  • Deep expertise in risk-based prioritization, continuous control monitoring, evidence-as-code automation, and framework-mapping rigor, using methodologies such as NIST RMF and ISO 31000 risk methodologies and quarterly control-effectiveness reviews to build audit-ready compliance posture and a defensible risk narrative for the board.
  • Engaged collaborator working cross-functionally with Engineering, IT, Legal, and Procurement teams in regulated SaaS and federal-contractor environments, sitting on risk committees, vendor reviews, and auditor walkthroughs from kickoff to the final report.
  • Emerging leader who raises the team’s bar for evidence completeness and control-documentation discipline through peer reviews, while running GRC enablement workshops and writing the policy and control-narrative templates the team reuses.

Technical Skills

Compliance Frameworks:
SOC 2 Type II, ISO 27001, NIST CSF 2.0, NIST SP 800-53 Rev 5, FedRAMP Moderate, CMMC 2.0, PCI DSS v4.0
Regulations & Privacy:
GDPR, CCPA/CPRA, HIPAA, Privacy Act, SOX, DPIAs, data mapping
Risk Management:
NIST RMF, FAIR, ISO 31000, ISO 27005, risk registers, business impact analysis, KRIs
Audit & Control Testing:
Control testing (TOD/TOE), evidence collection, auditor walkthroughs, sampling, ITGC testing, gap assessments, POA&M tracking
GRC Platforms & Automation:
ServiceNow IRM, Vanta, AuditBoard, Archer, Drata, Jira, Confluence, SQL, Python
Third-Party Risk:
OneTrust, SIG, CAIQ, vendor risk tiering, SOC report review, BitSight
Reporting & Analytics:
Power BI, Tableau, Excel (advanced), KRI/KPI dashboards, board reporting

Education

The George Washington University B.S. in Information Systems, concentration in Cybersecurity
Washington, DC • Sep 2014 - May 2018

Work Experience

Booz Allen Hamilton Senior GRC Analyst
McLean, VA • Apr 2022 - Present
  • Own compliance framework operations across federal-contracting environments spanning 10 product lines for DoD and civilian agencies, running FedRAMP Moderate, CMMC Level 2, and NIST 800-53 Rev 5 as 4 concurrent compliance programs.
  • Run enterprise and IT risk management for 150+ risks in the register, scoring them with NIST RMF in annual assessments and reporting posture quarterly to the Risk Committee and board; those briefings moved $2.4M of security budget to the top risks.
  • Lead internal and external audit coordination across 8 cycles per year, running auditor walkthroughs, evidence collection, and finding remediation; delivered SOC 2 Type II and FedRAMP ATO renewals with zero significant findings.
  • Own control design, testing, and continuous monitoring across 320+ in-scope controls, writing control narratives against NIST 800-53 with operating-effectiveness testing and compensating-control documentation, lifting control effectiveness from 87% to 99%.
  • Maintain the security and IT policy library across 45+ policies, standards, and procedures, running annual recertification cycles and role-based awareness training, with adoption across 12 business units.
  • Run third-party risk reviews for 220+ vendors and subcontractors through SIG and CAIQ questionnaires, SOC 2 report analysis, and contract security clauses with Legal and Procurement; found 30+ critical gaps that changed contract terms or vendor tiers.
  • Support the privacy program across 60+ systems, running HIPAA and Privacy Act data mapping, privacy impact assessments, and data request workflows with Legal and the privacy office; closed an agency audit finding within 90 days.
  • Led the GRC platform rollout on ServiceNow IRM and Vanta, automating evidence collection from AWS and Okta, control-status dashboards, and Jira finding workflows; cut the audit-prep cycle from 6 weeks to 9 days.
Grant Thornton GRC Analyst
Arlington, VA • Jul 2018 - Mar 2022
  • Tested SOX ITGCs for 9 public-company clients, walking through access, change, and operations controls in SAP and Oracle ERP and sampling evidence against PCAOB standards; cut repeat deficiencies by 40% over 2 audit cycles.
  • Ran SOC 2 readiness assessments for 14 SaaS clients, mapping their controls to the Trust Services Criteria in Excel and AuditBoard and writing gap remediation plans; 12 of them earned a clean Type I report on the first attempt.
  • Delivered security awareness and stakeholder enablement through annual all-hands training, targeted phishing and tabletop sessions, and compliance office hours reaching 4,500+ employees across 6 client engagements, partnering with Engineering, IT, HR, and Legal to ship 12 client-specific control documents and onboard 4 junior GRC analysts.
Done editing? Download a real PDF (selectable text, ATS-friendly, US Letter) or an editable Word file if a recruiter asks for one.

About this template

A GRC Analyst resume template, built by a tech recruiter.

A GRC Analyst keeps a company’s security program provable. You map controls to frameworks like SOC 2 and ISO 27001, keep the risk register current, collect evidence for the auditors, review vendors and write the policies everyone else is supposed to follow. It’s half security, half audit, and a big part of the job is getting busy engineers to hand you proof. If you’re writing a risk and compliance analyst resume, it’s the same job and the same template.

The problem is that most GRC resumes read the same. Everyone lists SOC 2, ISO 27001 and NIST, so a list of frameworks tells a recruiter almost nothing. What gets you the interview is proof that you ran the program. Think of the audits you got through (and with how many findings), the controls you tested, the risks you tracked to closure, the vendors you reviewed and the hours you saved by automating evidence.

I built this GRC resume template around that proof, with a bullet for each part of the GRC Analyst role profile so you don’t forget one. Under it you’ll find 3 finished GRC resumes and my 6 steps to write a GRC Analyst resume, section by section.

If your resume is already written, you don’t need a Reddit thread full of opinions on your GRC resume. I’ll read it the way I screened candidates at Google and tell you what’s missing. It’s a free tech resume review, and you get my notes back by email.

Industry signal

What the market says about GRC Analyst roles

If you’re wondering whether GRC is a good bet in 2026, look at the rule book. Public companies have had to report material cyber incidents to the SEC since December 2023. DORA has applied to EU banks and insurers since January 2025, the last PCI DSS 4.0 requirements became mandatory in March 2025, and most of the EU AI Act kicked in in August 2026. Each of those needs someone to map controls, collect evidence and report on risk. That someone is a GRC Analyst.

+21% US security analyst job growth, 2025 to 2035 US Bureau of Labor Statistics
$77,455 Average US GRC Analyst salary, October 2026 Salary.com
  • ISC2 @ISC2 · Cybersecurity nonprofit
    Governance, risk and compliance are business-critical priorities. As regulations evolve and organisations face growing scrutiny, #cybersecurity professionals play a key role in building trust and resilience: ow.ly/wh4T50ZPJu9 #GRC
  • Vanta @TrustVanta · Compliance automation platform
    💡 "AI is only as good as the governance around it, and right now governance is falling short." Khushboo Kashyap, our Senior Director of GRC, says in her @CityAM article that annual, point-in-time reviews can't keep up with how fast AI risk changes.
  • Phil Venables @philvenables · 4x CISO, Ballistic Ventures partner
    Why a "Control Failure" Should Trigger the Same Alarm as a Data Breach: From SRE to CRE We usually only hit the panic button when data is actively breached, but what if we treated a failed defense mechanism with that exact same intensity?
  • CompTIA @CompTIA · IT certification body
    AI is reshaping cybersecurity hiring, even when job titles haven't changed. SOC, cloud, GRC, and DevSecOps roles are absorbing AI responsibilities fast. See which cybersecurity roles SecAI+ helps you compete for: comptia.org/en-us/blog/job…

Resume Samples

GRC Analyst Resume Examples

Before you fill the template above, it helps to see a finished GRC Analyst resume. I wrote 3 GRC resume examples: a junior analyst two years into control testing at a Big 4 advisory firm (a good model for an entry-level GRC resume), a senior analyst running bank and insurer engagements, and a principal who owns the cyber risk program at a global beverage company. If you’re applying outside the US, use any of them as your GRC Analyst CV. You can download each one as a PDF or a Word file, free and with no signup.

Junior GRC Analyst Resume Example

What a junior GRC resume needs to show: the frameworks you’ve supported, the controls you’ve tested, the evidence you’ve collected, and Security+ or the cert you’re studying for.

Years of experience
2 years
Industry
Big 4 risk advisory
Stack
AuditBoardExcelJiraPower BI
Download PDF Download Word

Click to download the Junior GRC Analyst resume example as a PDF or a Word file. Free / No signup.

Hannah Schmidt

Junior GRC Analyst

New York, NY · hannah.schmidt@gmail.com · +1 212-555-0163 · linkedin.com/in/hannahschmidt

Profile Summary

  • Junior GRC Analyst with 2 years in Big 4 risk advisory serving fintech and SaaS clients, across SOX ITGC testing, SOC 2 readiness, and risk registers, specializing in control testing and evidence tracking.
  • Hands-on with frameworks (SOC 2, ISO 27001:2022, NIST CSF 2.0), GRC platform (AuditBoard), compliance automation (Vanta), workpapers (Excel), and reporting (Power BI), with working knowledge of Jira and SQL.
  • Growing strength in ITGC walkthroughs, attribute sampling, and framework mapping, using the firm's standard test scripts and tickmark conventions so engagement managers sign off with few review notes.
  • Partners with engagement managers, client IT leads, and control owners across 8 to 12 client engagements a year, from kickoff walkthroughs to the closing meeting where findings and management responses get agreed.
  • Built the ITGC walkthrough template and evidence request tracker that 6 analysts on the team now start every engagement from, and is studying for CISA on top of CompTIA Security+.

Technical Skills

Compliance Frameworks:
SOC 2 Type II, ISO 27001:2022, NIST CSF 2.0, PCI DSS v4.0 (basic), CIS Controls v8
Regulations & Privacy:
SOX, GDPR, CCPA/CPRA, GLBA, HIPAA (basic)
Risk Management:
Risk registers, NIST RMF, NIST SP 800-30, likelihood and impact scoring, risk treatment plans
Audit & Control Testing:
Design and operating effectiveness testing, ITGC walkthroughs, attribute sampling, evidence collection, gap assessments
GRC Platforms & Automation:
AuditBoard, Vanta, OneTrust (data mapping), Jira, Confluence, SQL (basic)
Third-Party Risk:
SIG Lite questionnaire, SOC report review, vendor risk tiering, Archer (vendor module)
Reporting & Analytics:
Excel (pivot tables, XLOOKUP), Power BI, status reporting, exception logs
Page 2 of 2

Work Experience

Deloitte Risk & Financial Advisory Junior GRC Analyst New York, NY · Sep 2024 to Present
  • Tested design and operating effectiveness of 146 SOX ITGCs at fintech clients, pulling attribute samples from Okta and Jira into AuditBoard workpapers, with 94% cleared on first review.
  • Tracked evidence requests for 4 SOC 2 Type II readiness projects in Jira with a Power BI status page for owners, so clients entered fieldwork with 96% closed.
  • Mapped a SaaS client's controls to SOC 2 and ISO 27001:2022 Annex A in an Excel matrix, finding 23 missing controls in the gap assessment before certification began.
  • Set up Vanta for a Series B client, connecting AWS, Okta, and GitHub, then mapping its tests to SOC 2 criteria, so 61% of evidence moved off screenshots.
  • Built a risk register for a 250-person payments client from owner interviews, scoring likelihood and impact per NIST SP 800-30 in Excel, logging 38 risks with treatment owners.
American Express Technology Risk Intern New York, NY · Jun 2023 to Aug 2023
  • Reviewed SIG Lite questionnaires and SOC 2 reports for 27 marketing vendors, scoring each against the vendor tiering model in Archer and escalating 6 rated high risk.
  • Updated GDPR Article 30 records of processing for 3 card-member apps, tracing personal data fields with product owners in OneTrust data maps and closing 11 missing entries.
  • Simplified the data classification standard and 4 procedures into plain language for the annual policy refresh, then built a Microsoft Forms quiz that 1,300 technology staff completed.

Education

New York University, Stern School of Business B.S. in Business (Information Systems and Accounting) New York, NY · Sep 2020 to May 2024
CompTIA Security+ certification New York, NY · Mar 2025

Senior GRC Analyst Resume Example

What a senior GRC resume needs to show: a framework you own from readiness to report, the vendor reviews you run, and the risks you take to leadership.

Years of experience
6 years
Industry
Financial services
Stack
OneTrustSecurityScorecardPythonPower BI
Download PDF Download Word

Click to download the Senior GRC Analyst resume example as a PDF or a Word file. Free / No signup.

Omar Khalifa

Senior GRC Analyst

Chicago, IL · omar.khalifa@gmail.com · +1 312-555-0149 · linkedin.com/in/omarkhalifa

Profile Summary

  • Senior GRC Analyst with 6 years in financial services cyber risk, advising banks, asset managers, and insurers on NYDFS Part 500, SOX ITGC, and vendor risk, specializing in gap assessments and remediation roadmaps.
  • Hands-on across GRC platform (Archer), vendor risk (OneTrust TPRM and SecurityScorecard), risk method (FAIR), testing scripts (Python and SQL), and dashboards (Power BI), plus working knowledge of ServiceNow IRM and DORA.
  • Specialist in FAIR quantification, full-population ITGC testing, and vendor tiering, using Monte Carlo loss ranges and Python test scripts so bank boards get dollar figures and tested evidence, not heat maps.
  • Runs client meetings with CISOs, heads of internal audit, and procurement leads across 7 to 9 engagements a year, and presents findings at the risk committees that approve remediation budgets.
  • CISA holder who has coached 3 associates to promotion and maintains the Python test library for access and change controls that the Chicago cyber practice runs on every SOX engagement.

Technical Skills

Compliance Frameworks:
NIST CSF 2.0, ISO 27001:2022, SOC 2 Type II, PCI DSS v4.0, NIST SP 800-53, CIS Controls v8
Regulations & Privacy:
NYDFS Part 500, SOX, GLBA, GDPR, CCPA/CPRA, HIPAA, DORA (working knowledge)
Risk Management:
FAIR, NIST RMF, ISO 27005, risk registers, KRIs, risk treatment plans
Audit & Control Testing:
SOX ITGC testing, full-population testing, sampling, design and operating effectiveness, remediation tracking
GRC Platforms & Automation:
Archer, OneTrust TPRM, ServiceNow IRM (working knowledge), Python (pandas), SQL, Jira
Third-Party Risk:
SIG Core and Lite, CAIQ, vendor risk tiering, SOC report review, SecurityScorecard, contract security clauses
Reporting & Analytics:
Power BI, Excel, KRI/KPI reporting, risk committee decks
Page 2 of 2

Work Experience

KPMG Cyber Security Services Senior GRC Analyst Chicago, IL · Jul 2022 to Present
  • Led NYDFS Part 500 gap assessments at 9 banks and insurers, mapping controls to NIST CSF 2.0 in Excel, with roadmaps that closed 71% of gaps in 12 months.
  • Quantified a regional bank's top cyber risks with FAIR and Monte Carlo runs in Python, swapping heat-map colors for loss ranges that moved $3.2M into identity and backup controls.
  • Replaced sample-based SOX ITGC access testing at 3 banks with full-population checks in Python and SQL against Active Directory and Workday, cutting testing hours per cycle by 38%.
  • Rebuilt vendor tiering for a top-20 insurer's 1,400 suppliers in OneTrust, sending SIG Core only to the top tier and adding SecurityScorecard alerts, cutting review backlog by 64%.
  • Designed a Power BI remediation dashboard on a client's Archer issues module, with aging buckets and owner views, which brought past-due findings from 86 to 19 in two quarters.
Northern Trust IT Risk Analyst Chicago, IL · Jul 2020 to Jun 2022
  • Coordinated evidence for the asset-servicing SOC 1 Type II audit, holding weekly PBC reviews with control owners in Archer, which cut exceptions from 11 to 3 in one cycle.
  • Revised 6 IT security standards against NIST SP 800-53 Rev. 5 and ran the policy exception process in ServiceNow with 90-day expiry, cutting open exceptions from 140 to 52.
  • Owned GDPR DPIAs in OneTrust for 12 wealth-management features with the privacy office, adding a 10-question pre-screen that cut average review time from 5 weeks to 2.

Education

University of Illinois Chicago M.S. in Information Assurance Chicago, IL · Aug 2018 to May 2020
ISACA Certified Information Systems Auditor (CISA) Chicago, IL · Nov 2022

Principal GRC Analyst Resume Example

What a principal GRC resume needs to show: a program that spans several frameworks, the analysts you lead, and risk reporting that reaches the board.

Years of experience
12 years
Industry
Consumer goods and retail
Stack
AuditBoardOneTrustMicrosoft PurviewPower BI
Download PDF Download Word

Click to download the Principal GRC Analyst resume example as a PDF or a Word file. Free / No signup.

Reema Banerjee

Principal GRC Analyst

Atlanta, GA · reema.banerjee@gmail.com · +1 404-555-0172 · linkedin.com/in/reemabanerjee

Profile Summary

  • Principal GRC Analyst with 12 years in Fortune 500 consumer goods and retail, across enterprise cyber risk, SOX ITGC, PCI DSS, and global privacy, specializing in unified control frameworks and board risk reporting.
  • Fluent across GRC platform (AuditBoard), privacy and data protection (OneTrust and Microsoft Purview), vendor ratings (BitSight), risk method (FAIR), and reporting (Power BI), with deep knowledge of the SEC cyber disclosure rules.
  • Deep expertise in control rationalization, loss-based risk quantification, and continuous control monitoring, using the Secure Controls Framework and FAIR to run one compliance program that answers several regulators at once.
  • Reports to the CISO and works with the Chief Privacy Officer, internal audit, and procurement, chairing the monthly cyber risk forum and drafting the 10-K Item 1C disclosure with legal.
  • Manages a team of 5 GRC analysts, holds CISSP and CRISC, and built the control library, risk taxonomy, and board reporting pack the cyber program now runs on.

Technical Skills

Compliance Frameworks:
NIST CSF 2.0, ISO 27001:2022, PCI DSS v4.0, SOC 2 Type II, NIST SP 800-53, Secure Controls Framework
Regulations & Privacy:
SOX, SEC cyber disclosure rules, GDPR, CCPA/CPRA, NIS2, ISO 27701
Risk Management:
FAIR, NIST RMF, ISO 31000, enterprise risk taxonomy, KRIs, business impact analysis
Audit & Control Testing:
SOX ITGC, continuous control monitoring, design and operating effectiveness, PCI DSS Report on Compliance
GRC Platforms & Automation:
AuditBoard (CrossComply, ITRM), ServiceNow IRM, Archer, OneTrust, Microsoft Purview, ACL Analytics
Third-Party Risk:
BitSight, SIG Core, vendor risk tiering, SOC report review, contract security clauses, fourth-party mapping
Reporting & Analytics:
Power BI, Audit Committee reporting, KRI/KPI dashboards, Excel
Page 2 of 2

Work Experience

The Coca-Cola Company Principal GRC Analyst Atlanta, GA · Mar 2019 to Present
  • Unified NIST CSF 2.0, ISO 27001:2022, PCI DSS v4.0, and SOX ITGC into one control set on the Secure Controls Framework, cutting duplicate evidence requests by 57%.
  • Brief the Audit Committee quarterly on the top 10 cyber risks, scored with FAIR and tracked in Power BI, tying $18M of security spend to modeled loss reduction.
  • Migrated GRC from Archer to AuditBoard CrossComply and ITRM, wiring Entra ID, Workday, and ServiceNow CMDB integrations that now collect evidence for 46% of controls automatically.
  • Shifted 2,300 suppliers from annual questionnaires to continuous monitoring, opening a OneTrust review whenever a BitSight rating drops, cutting critical-vendor recheck time from 11 months to 9 days.
  • Rewrote the global security policy set in plain language, cutting it from 58 documents to 19, and tied data classification to Microsoft Purview labels in Outlook and Teams.
The Home Depot Senior IT Risk Analyst Atlanta, GA · Jun 2014 to Feb 2019
  • Managed the PCI DSS 3.2 Report on Compliance for 2,200 stores with the QSA, building a store-sampling evidence plan in SharePoint that cut findings from 14 to 2.
  • Automated 85 SOX ITGC tests on SAP and Active Directory in ACL Analytics, running them weekly instead of quarterly to catch failing controls between audits, cutting deficiencies by 62%.
  • Kicked off CCPA readiness with legal and marketing, mapping personal data across 31 customer systems in OneTrust and finding 9 with no retention rule before the 2020 deadline.

Education

Georgia Institute of Technology M.S. in Computer Science Atlanta, GA · Aug 2012 to May 2014
ISC2 and ISACA CISSP and CRISC Atlanta, GA · 2017 and 2020

Free resume review

A recruiter screen, but with feedback

You applied to hundreds of jobs: no result. Companies won’t give you feedback, so you’re stuck in a loop. Rejections will keep coming until you know what’s wrong.

Let’s break this cycle today!

I’ll screen your resume the same way I did at Google.

You’ll get:

  • Your resume sections and content scored.
  • A clear list of what to improve, why, and how.
  • Behind the scenes secrets on the screening process.

How I rewrite GRC Analyst resumes

How to write a GRC Analyst resume

Emmanuel Gendre, ex-Google recruiter

Emmanuel Gendre Ex-Google recruiter, tech resume writer

Before I started writing resumes full time, I recruited for 13 years, many of them at Google. GRC resumes come across my desk all the time, and most of them have the same problem: years of real program work, boiled down to a list of frameworks.

When I rewrite one through my tech resume writing service, I go over every single word. If you’re doing it yourself, though, focus on these 6 steps. Here’s the order I’d go in.

  1. Step 1 Format & layout One column, plain section names, sent as a PDF. Go to step 1
  2. Step 2 Profile Summary 5 bullets that decide whether the recruiter keeps reading. Go to step 2
  3. Step 3 Work Experience Your current role, mapped to the 8 areas of the GRC role profile. Go to step 3
  4. Step 4 Bullet Points My 5-level method, from a plain task to a bullet with a number. Go to step 4
  5. Step 5 Technical Skills 7 categories, a keyword finder and the soft skills to prove. Go to step 5
  6. Step 6 Keywords & Metrics Match the job description’s keywords and back every bullet with a number. Go to step 6

Step 1 · Format & Layout

GRC Analyst resume format and layout

Let’s start with the easiest win. Before anyone reads your bullets, software has to read your file and a recruiter has to find your experience fast. Three things decide both: ATS compliance, the layout, and the file you send.

01ATS Compliance

ATS compliance for your GRC Analyst resume

Most companies run every application through an Applicant Tracking System (ATS). It pulls your text into fields (titles, dates, employers, skills) and matches it against the job description, and GRC postings often filter on framework names like SOC 2, ISO 27001 or NIST 800-53. If the parser can’t read your layout, those keywords don’t count, and you can be rejected before a person ever sees your resume. I explain how ATS software reads a resume in a separate article. Here, an ATS-friendly GRC resume comes down to 3 rules:

The 3 rules
  1. Use a 100% text based format (no Canva!)

  2. Avoid tables, pictures, and complex structures.

  3. Use the most predictable section names, like “Profile Summary” and “Work Experience”

02Design & Layout

GRC Analyst resume design and layout

Something I learned at Google: recruiters hate fancy designs. After a few dozen resumes in a row, you know exactly where the job title, the dates and the frameworks should sit. Sidebars, icons and progress bars make you search for them, and that search eats into the few seconds each resume gets.

So pick a boring, predictable layout and let the audit results stand out. That’s how the template above is set up, and these are its specs if you’re building your own.

Layout Spec
Columns
One. No sidebars, tables, columns, pictures or tabs.
Margins
0.7 in on all four sides
Body size
10 to 11 pt
Type
One family, weight for hierarchy
Length
One page under 5 years, two after
Section order
Summary, Skills, Experience, Education
PDF

03File Format

Resume file format for your GRC Analyst resume

Send your GRC resume as a PDF by default, and as a Word doc only when a posting asks for it. ATS software reads PDF text reliably, the formatting can’t shift on someone else’s computer, and no one can edit a line by mistake before it reaches the hiring manager. If a recruiter wants Word, use the Word download in the template instead of converting your PDF. My article on which resume file format to use compares every option.

Format Guide
PDF
Your default. Layout holds, text stays selectable.
Word (.docx)
When the posting or a recruiter asks for it. Use the Word download above.
Plain text
For portals that make you paste into a box
Never
Images, scans, password-protected PDFs, shared-drive links
File name
Avery-Singh-GRC-Analyst.pdf

Step 2 · Profile Summary

GRC Analyst profile summary

Yes, you need a profile summary, even as a junior. It replaces the old GRC Analyst resume objective, because recruiters care about what you’ve done, not what you’re hoping to find. They screen in two steps: a quick first read to pick the relevant candidates, then a closer read to build the interview shortlist. You only get a few seconds in that first read, and the summary is where they spend them.

In a GRC resume summary, those 5 bullets need to show three things fast: which frameworks you’ve run, how big the program was, and whether auditors and engineers can work with you. Each bullet has its own job, and here’s the list. The full method is in my guide on how to write a profile summary.

  1. 1

    Title, years and scope

    Your target title, your years of experience, the kind of environment you’ve worked in (SaaS, banking, federal) and the programs you specialize in. A recruiter should know your level by the end of the line.

  2. 2

    Your stack

    The frameworks, GRC platform, risk method and privacy rules you use, each introduced by its category: frameworks (SOC 2, ISO 27001), platform (Vanta), risk (NIST RMF). It’s the line ATS keyword matching hits first.

  3. 3

    Domain expertise

    The parts of the role profile you’re strongest in, the methods behind them (control testing, FAIR scoring, continuous monitoring) and what they produced. This is where “knows SOC 2” becomes “runs the program”.

  4. 4

    Collaboration

    Who you work with every week (engineering, IT, legal, procurement, external auditors) and where you show up: risk committees, vendor reviews, audit walkthroughs. GRC is a people job, and recruiters check for it.

  5. 5

    Leadership

    What you leave behind: policy templates, the audit playbook, the juniors you trained. You don’t need to manage anyone for this one. It tells a recruiter you’ll make the team better, not just close tickets.

GRC Analyst resume summary example, from the template above
  • Senior GRC Analyst with 8 years of experience running regulated and federal-contracting environments across federal contracting, SaaS, and financial services, specializing in multi-framework compliance, risk management, and audit readiness.
  • Hands-on coverage across compliance frameworks (SOC 2, ISO 27001, FedRAMP), risk frameworks (NIST RMF), GRC platforms (ServiceNow IRM, Vanta), third-party risk (OneTrust), privacy (GDPR), and analytics (SQL, Excel), with strong fundamentals in control-narrative writing and audit-ready documentation.
  • Deep expertise in risk-based prioritization, continuous control monitoring, evidence-as-code automation, and framework mapping, using NIST RMF and ISO 31000 and quarterly control-effectiveness reviews to build an audit-ready compliance posture and a defensible risk story for the board.
  • Engaged collaborator working cross-functionally with Engineering, IT, Legal, and Procurement in regulated SaaS and federal-contractor environments, sitting on risk committees, vendor reviews, and auditor walkthroughs from kickoff to the final report.
  • Emerging leader who raises the team’s bar for evidence completeness and control-documentation discipline through peer reviews, while running GRC enablement workshops and writing the policy and control-narrative templates the team reuses.

Step 3 · Work Experience

GRC Analyst work experience

Remember the closer read from Step 2? That’s this step. The recruiter goes through your experience in more detail now, but most of the decision is made on your most recent role.

That’s logical: your current job is the best picture of what you can do today. So it has to cover the whole GRC Analyst role profile (the list of core competencies recruiters screen against), with one bullet per area. Here are the 8 areas. The template above already gives each one its own bullet.

GRC Analyst role profile
  1. Compliance Framework Programs

    You run the framework programs that let the company sell to enterprise customers. A missing SOC 2 report can hold up a deal for months, so hiring managers want someone who has operated frameworks, not just studied them. Show how you used control mapping and gap assessments across SOC 2 and ISO 27001 to get certified and stay certified.

    Techniques
    control mapping, gap assessments, audit scoping
    Tools
    SOC 2, ISO 27001:2022, NIST CSF 2.0, FedRAMP
    Metrics
    frameworks run, certifications kept, controls mapped
  2. Risk Assessment & Reporting

    You keep the risk register honest and put risk in front of leadership. A register nobody updates isn’t worth much, and executives only fund what they understand, so recruiters look for regular reporting to real decision makers. Explain how you used NIST RMF or FAIR scoring and quarterly reporting to move budget toward the top risks.

    Techniques
    risk scoring, treatment plans, exception reviews
    Tools
    NIST RMF, FAIR, ISO 27005, ServiceNow IRM
    Metrics
    risks tracked, risks closed, budget moved
  3. Audit Readiness & Evidence

    You get the company through its audits without a last-minute panic. Auditors judge the whole security team by how fast the evidence shows up, and a clean report is something a hiring manager can show the CFO. Describe how you used an evidence calendar and auditor walkthroughs, in Vanta or AuditBoard, to finish audits with fewer findings.

    Techniques
    evidence request tracking, walkthroughs, finding remediation
    Tools
    AuditBoard, Vanta, Drata, Jira
    Metrics
    audits completed, findings per audit, prep time
  4. Control Testing & Monitoring

    You test whether controls actually work between audits. A control that only works in audit week isn’t really a control, and steady testing is what separates a real program from paperwork. Point out how you used design and operating effectiveness testing, plus automated monitoring, to catch failing controls earlier.

    Techniques
    design and operating effectiveness testing, sampling, continuous monitoring
    Tools
    NIST SP 800-53, AWS Config, Vanta, ServiceNow IRM
    Metrics
    controls tested, control effectiveness, time to fix
  5. Policy, Standards & Awareness

    You write the policies people actually follow, then train them on it. Auditors ask for the policy first and proof that employees know it second, so hiring managers want both the library and the training behind it. Mention how you used an annual review cycle and role-based training, mapped to ISO 27001, to raise adoption and cut exceptions.

    Techniques
    annual policy reviews, exception handling, awareness campaigns
    Tools
    Confluence, KnowBe4, ISO 27002, NIST CSF 2.0
    Metrics
    policies maintained, training completion, open exceptions
  6. Third-Party & Vendor Risk

    You check vendors before they get anywhere near customer data. Plenty of breaches now start at a supplier, so recruiters want to see risky vendors caught at review, not after an incident. Walk them through how you used vendor tiering and SIG or CAIQ questionnaires, with OneTrust or BitSight, to finish reviews on time and block the risky ones.

    Techniques
    vendor tiering, security questionnaires, SOC report reviews
    Tools
    SIG, CAIQ, OneTrust, BitSight
    Metrics
    vendors reviewed, review turnaround, high-risk vendors blocked
  7. Privacy & Data Protection

    You make sure customer data is handled the way the law says. A missed data request deadline or a skipped DPIA can turn into a fine, so hiring managers look for privacy work with dates and counts attached. Detail how you used DPIAs, data mapping and request workflows, under GDPR, CCPA or HIPAA, to hit every deadline.

    Techniques
    DPIAs, data mapping, data subject requests
    Tools
    OneTrust, GDPR, CCPA/CPRA, HIPAA
    Metrics
    requests answered on time, DPIAs completed, systems mapped
  8. Compliance Automation

    You automate the evidence work that used to take weeks of screenshots. Companies buy platforms like Vanta and Drata to cut audit prep, and they want analysts who can configure them, not just log in (some postings call this GRC engineering). Tell them how you used platform integrations and Python or SQL scripts to cut prep time and retire the compliance spreadsheet.

    Techniques
    evidence automation, integrations, dashboards
    Tools
    Vanta, Drata, ServiceNow IRM, Python
    Metrics
    audit prep time, controls automated, hours saved

On a GRC consultant resume, write each bullet around a client engagement: the framework, the client’s industry and the result. No GRC job yet? Put GRC projects on your resume as their own entry: a NIST CSF 2.0 self-assessment for a nonprofit, a risk register for a made-up company, or a GRC engineering project like a Python script that pulls audit evidence from AWS. Done right, your current role can run to 8 bullets or more, and that’s fine. Recruiters don’t mind length. They mind filler, which is what Step 4 is about.

Submit your resume for a free review!

Step 4 · Bullet Points

GRC Analyst resume bullet points

Bullet points take up more of my writing time than any other section, so I built a method for them: the Level System. It started from Google’s XYZ formula, but it goes further and it’s made for technical resumes. The full version is in my guide on writing resume bullet points.

It works in 5 levels. Each level asks you a question, and your answer is the detail you add to the bullet. For a GRC Analyst, the number at the end is usually an audit result, a control effectiveness rate, a prep time or a risk figure. You’ll find 24 more GRC resume bullet examples in the metrics table in Step 6.

  1. Level 1Task

    What did I work on? Start with one project you actually finished. On its own, a task gives a recruiter no reason to keep reading.

    Rolled out a new GRC platform.

  2. Level 2+ Techniques

    How did I do it? Techniques show you made decisions instead of following a checklist.

    Rolled out a new GRC platform, automating evidence collection and control-status tracking.

  3. Level 3+ Tools

    What tools did I use? Write down the actual products. It’s the cheapest keyword win on the whole resume.

    Rolled out a new GRC platform on ServiceNow IRM and Vanta, automating evidence collection from AWS and Okta and control-status tracking in Jira.

  4. Level 4+ Method

    What method did I follow? Add the framework you worked against. Most candidates skip it, and it tells the hiring manager how you work.

    Rolled out a new GRC platform for the FedRAMP Moderate program on ServiceNow IRM and Vanta, automating evidence collection from AWS and Okta and control-status tracking in Jira against NIST SP 800-53 Rev 5.

  5. Level 5+ Metric

    What was the result? Finish on one number. It turns a claim into proof, and it’s what gets you the call.

    Rolled out a new GRC platform for the FedRAMP Moderate program on ServiceNow IRM and Vanta, automating evidence collection from AWS and Okta and control-status tracking in Jira against NIST SP 800-53 Rev 5, and cut audit prep from 6 weeks to 9 days.

    1. 01 Task What you worked on
    2. 02 Techniques How you did it
    3. 03 Tools The stack you used
    4. 04 Method The method you followed
    5. 05 Metric The result, one number

Most GRC Analysts already have the numbers. They’re sitting in the audit report, the risk register or the GRC platform’s dashboard. Nobody’s told them those numbers belong on a resume. The bullet I see most often on GRC resumes is “Supported the SOC 2 audit.” No scope, no auditor, no result. Level 5 is how you fix it.

Step 5 · Technical Skills

GRC Analyst resume skills

The GRC resume skills that matter most are the frameworks you’ve run (SOC 2, ISO 27001, NIST CSF), risk assessment, audit and control testing, a GRC platform, third-party risk, privacy rules and reporting. The ATS reads this section and some recruiters filter on it, so copy the job description’s wording. If the posting says “SOC 2 Type II”, don’t write “audit frameworks”.

That said, this is the final touch. Your summary and bullets do the heavy lifting, and every skill you list here should show up in at least one of them. Below you’ll find the 7 categories of GRC skills I put on a resume, a finished example and the soft skills worth proving. Keywords get their own step next.

The 7 skill categories for a GRC Analyst resume

Starred items are the ones I’d put first: they show up on most GRC job descriptions. Keep one row per category, right under your summary, and skip labels like “Expert in SOC 2”. A recruiter can’t check them, so they just take up room.

Compliance Frameworks

The frameworks you’ve operated, with the version when it matters (ISO 27001:2022, PCI DSS v4.0).

SOC 2 Type IIISO 27001:2022NIST CSF 2.0NIST SP 800-53PCI DSS v4.0FedRAMPHITRUST CSFCIS Controls v8CMMC 2.0

Regulations & Privacy

The laws and rules your programs answer to. Only list the ones you’ve worked on.

GDPRHIPAACCPA/CPRASOXGLBADORANIS2SEC cyber disclosure rulesISO 27701

Risk Management

How you find, score and track risk, from the register to quantitative models.

Risk registersNIST RMFFAIRISO 31000ISO 27005Business impact analysisKRIsRisk treatment plans

Audit & Control Testing

The audit work itself. Recruiters check this row against your bullets.

Control testing (design and operating effectiveness)Evidence collectionAuditor walkthroughsSamplingITGC testingGap assessmentsRemediation tracking

GRC Platforms & Automation

The platforms you’ve configured, plus the scripting you use to automate evidence.

VantaAuditBoardServiceNow IRMDrataArcherOneTrustHyperproofWorkivaJiraConfluencePythonSQL

Third-Party Risk

The questionnaires, ratings and reviews you use to vet suppliers.

SIG questionnaireVendor risk tieringCAIQSOC report reviewSecurityScorecardBitSightContract security clauses

Reporting & Analytics

How you turn compliance and risk data into something leadership reads.

Power BIExcelTableauRisk dashboardsKRI/KPI reportingBoard reporting

A finished GRC Analyst skills section

Technical Skills sample, from the template above
Compliance Frameworks
SOC 2 Type II, ISO 27001, NIST CSF 2.0, NIST SP 800-53 Rev 5, FedRAMP Moderate, CMMC 2.0, PCI DSS v4.0
Regulations & Privacy
GDPR, CCPA/CPRA, HIPAA, Privacy Act, SOX, DPIAs, data mapping
Risk Management
NIST RMF, FAIR, ISO 31000, ISO 27005, risk registers, business impact analysis, KRIs
Audit & Control Testing
Control testing (TOD/TOE), evidence collection, auditor walkthroughs, sampling, ITGC testing, gap assessments, POA&M tracking
GRC Platforms & Automation
ServiceNow IRM, Vanta, AuditBoard, Archer, Drata, Jira, Confluence, SQL, Python
Third-Party Risk
OneTrust, SIG, CAIQ, vendor risk tiering, SOC report review, BitSight
Reporting & Analytics
Power BI, Tableau, Excel (advanced), KRI/KPI dashboards, board reporting

Soft skills for a GRC Analyst resume

Don’t list soft skills in your skills section. Prove them in a bullet instead. These are the 5 I look for on a GRC resume, each paired with a bullet that proves it.

  • Holding steady when an auditor pushes back

    Resume bulletDefended 14 control designs in SOC 2 Type II walkthroughs, getting 3 proposed exceptions withdrawn with supporting evidence.

  • Writing policy and risk in plain language

    Resume bulletRewrote a 40-page access control policy into a 6-page standard, cutting exception requests by half the next year.

  • Saying no to a risky vendor or exception

    Resume bulletBlocked 2 high-risk vendors after failed SOC report reviews, and agreed compensating controls with 5 others instead of a blanket waiver.

  • Getting busy engineers to hand over evidence

    Resume bulletSet up a monthly evidence calendar with 9 engineering teams, cutting late audit requests from 30% to under 5%.

  • Briefing executives and the board

    Resume bulletPresented quarterly risk posture to the board risk committee, which approved $1.1M for the top 3 risks.

Step 6 · Keywords & Metrics

GRC Analyst resume keywords and metrics

This last step is a final check on two things recruiters scan for. Keywords are the words ATS software filters on, so yours need to match the job description. Metrics are the numbers that make a recruiter believe your bullets.

Below you’ll find the GRC resume keywords that matter most, sorted into 3 tiers, a finder to check them against a real job posting, and the metrics that prove your bullets.

+42%

GRC Analyst resume keywords, ranked

Tap a keyword to see how it usually shows up in a job description, so you can spot it even when the wording changes.

Must-have

7

Put these in your summary, in at least one bullet and in your skills section.

In a job description“Own the governance, risk, and compliance program”

Strong supporting

10

Add the ones you’ve actually done, in a bullet or in your skills.

In a job description“Design and operating effectiveness testing”

Bonus

8

Worth listing when they’re true. They help you stand out, not get through.

In a job description“Moderate or High authorization scope”

Extract GRC Analyst keywords from a job description

Paste a GRC, compliance or IT risk job description in the box. You’ll get the frameworks, regulations, platforms and audit terms it asks for, ranked by importance, so you know what to add to your skills and bullets. Want to do it by hand? Open 5 postings at your level, circle any term you see in at least 3 of them, and make sure each one shows up in a bullet.

Must-have
Put these in your skills section and back each one with a bullet.
Strong supporting
Add the ones you’ve actually worked with. Skip the rest.

Nothing is uploaded: it all happens in your browser.

Metrics for a GRC Analyst resume

Pick one metric per bullet. Here are 3 for each area of the role profile, each next to a resume bullet that uses it.

MetricExample bullet
Compliance Frameworks
Frameworks run Count Frameworks your program certifies against.Ran SOC 2, ISO 27001 and PCI DSS from one control set, replacing 3 separate evidence cycles.
Control mapping Percent Required controls mapped to an owner and evidence.Mapped all 93 ISO 27001:2022 Annex A controls to evidence owners ahead of certification.
Scope growth Count Frameworks or business units added over time.Grew the program from 1 framework to 3 (SOC 2, ISO 27001 and HIPAA) in 18 months.
Risk Assessment
Risks tracked Count Risks in the register with an owner and a treatment plan.Built a register of 140 scored risks, each with an owner and a treatment date.
Risks reduced Count Top risks closed or brought within appetite.Brought 9 of the top 10 enterprise risks within board appetite in one year.
Reporting cadence Frequency How often leadership sees risk posture.Moved board risk reporting from annual slides to a monthly Power BI dashboard.
Audit Readiness
Audit results Count How your audits came back.Delivered 2 consecutive SOC 2 Type II reports with zero exceptions.
Findings closed Time How fast audit findings get fixed.Cut average audit finding remediation from 90 days to 21.
Audit prep time Time Time from kickoff to evidence ready.Cut SOC 2 audit prep from 6 weeks to 9 days with automated evidence requests.
Control Testing
Controls tested Count In-scope controls tested on a schedule.Tested all 320 in-scope NIST 800-53 controls every quarter.
Control effectiveness Percent Controls operating as designed when tested.Raised control effectiveness from 87% to 99% over 2 testing cycles.
Controls automated Count Checks that run without a person.Automated continuous monitoring for 80 cloud controls in Vanta and AWS Config.
Policy & Awareness
Policies current Count Policies reviewed on schedule and mapped to controls.Brought all 45 security policies current and mapped each one to ISO 27001 controls.
Training completion Percent Staff who finished security training.Raised awareness training completion from 71% to 99% across 4,500 employees.
Phishing click rate Percent Staff who click a simulated phishing email.Cut the phishing simulation click rate from 18% to 3% in a year.
Vendor Risk
Vendors assessed Count Third parties reviewed and tiered.Assessed and tiered 300+ vendors in OneTrust ahead of contract renewals.
Review turnaround Time Time to clear a vendor for use.Cut vendor security reviews from 3 weeks to 4 days with tiered questionnaires.
Risky vendors caught Count High-risk vendors blocked or fixed before signing.Blocked 6 high-risk vendors at review and got fixes from 14 more before signing.
Privacy
Requests on time Percent Data subject requests answered by the deadline.Answered all 240 data subject requests inside the GDPR one-month deadline.
DPIAs before launch Count Privacy reviews done before a feature ships.Ran 35 DPIAs with product teams before launch, with no regulator findings.
Systems mapped Count Systems in the record of processing.Mapped personal data across 60 systems for the record of processing activities.
Compliance Automation
Evidence automated Count Evidence collected without screenshots.Automated evidence collection for 200+ controls through Vanta integrations.
Hours saved Time Analyst time freed by automation.Saved about 400 analyst hours a year by scripting evidence pulls in Python.
Platform adoption Count Control owners working in the platform, not spreadsheets.Moved 40 control owners from spreadsheets to ServiceNow IRM in one quarter.

What if you don’t have exact numbers?

  • 1

    Look where the numbers already live. Audit reports, the risk register, your GRC platform’s dashboards and Jira hold most of them.

  • 2

    Estimate honestly, then round down. “About 200 controls” beats no number, as long as you can explain how you got it in an interview.

  • 3

    Use scope when you can’t measure results. Frameworks, systems, vendors or teams covered still tell a recruiter how big your program was.

Free resume review

A recruiter screen, but with feedback

You applied to hundreds of jobs: no result. Companies won’t give you feedback, so you’re stuck in a loop. Rejections will keep coming until you know what’s wrong.

Let’s break this cycle today!

I’ll screen your resume the same way I did at Google.

You’ll get:

  • Your resume sections and content scored.
  • A clear list of what to improve, why, and how.
  • Behind the scenes secrets on the screening process.

Frequently asked

GRC Analyst resume FAQ

Four sections: a 5-bullet profile summary, technical skills grouped by category (frameworks, regulations, risk, audit, GRC platforms, vendor risk, reporting), education with your certifications (CISA, CRISC or Security+), and work experience with one bullet for each area of the role profile.

Follow the 6 steps above in order: format, summary, work experience, bullet points, skills, then keywords and metrics. If you’re stuck, write your work experience first. The summary is much easier once your bullets exist.

Yes. No signup, no email, no paywall. The PDF and Word downloads are free too.

Yes. Click Word above the template to get your GRC resume as an editable Word doc (.docx), or download any of the 3 examples as a Word file.

Yes. One column, standard section names (Profile Summary, Technical Skills, Education, Work Experience), no tables, no graphics. That’s the format parsers like Workday and Greenhouse handle best. To test your own version, upload it to the free ATS checker.

One page if you have under 5 years of experience, two pages after that. Recruiters don’t mind a second page full of audits and programs. They mind filler.

They help, but most analyst roles don’t require them. CISA and CRISC carry the most weight for audit and risk work, CISSP for security-heavy programs, and ISO 27001 Lead Auditor for ISO shops. CISM fits a move toward program management, and CIPP/US (from the IAPP) fits privacy-heavy roles. List them under Education, and add any you’re working toward with the expected date.

Audit results (findings per audit, clean reports), control effectiveness, audit prep time, risks tracked and closed, vendor reviews and their turnaround, and data requests answered on time. Use one per bullet, and put the most impressive one first in each job.

A SOC Analyst resume is about detecting and responding to threats, and a Security Engineer resume is about building controls into systems. A GRC Analyst resume is about proving those controls exist and work: frameworks, audits, risk, vendors and policy. An IT Auditor resume shows you testing those controls as the independent reviewer, for internal audit or an audit firm, while a GRC Analyst runs the program that gets audited. If you do some of each, lead with whatever the job posting asks for most. If you’re closer to one of the other jobs, start from my SOC Analyst resume template or my Security Engineer resume template instead.

Look for postings titled junior or associate GRC Analyst. Use the same template, keep it to one page, and lead with the frameworks you’ve touched in internships, audit support or IT work. If you don’t have GRC experience yet, add 2 or 3 of the GRC projects from Step 3. The junior example above shows how it looks with 2 years of experience.

Lead with whatever the posting leans on. If it talks about audits, frameworks, vendors and board reporting, put your program work first. If it asks for cloud controls, evidence automation or scripting, open with that and back it up with your framework experience. A plain GRC Analyst posting usually wants the program side first.

No. Recruiters screen the content, not where the layout came from. What hurts is a template full of generic compliance language, which is exactly what the placeholders are there to replace.

More resources

More help with your GRC Analyst resume